Is your old Drupal site quietly selling spam?
Yesterday I came across a really good example of what can happen to an old EOL Drupal website, so I thought it was worth writing up.
 Mike DixonSenior Mind · · 1 min read

Why we keep banging on about upgrades
A decent chunk of our work here at ComputerMinds is Drupal upgrades. Usually it's a site that's been left alone for a while, nobody has quite got round to it, and it's ended up on a version of Drupal that is no longer supported.
We don't just do upgrades for fun. OK, we do get paid for them too, but let's not ruin the article. The real reason we push them is that leaving a site on an end-of-life (EOL) version of Drupal is a security problem, not a box-ticking one.
Yesterday I came across a really good example of why, so I thought it was worth writing up.
A real example from yesterday
I won't name the site, obviously. But when I looked at the source of the homepage, there were multiple snippets sitting in the page. The site owners had no idea they were there.
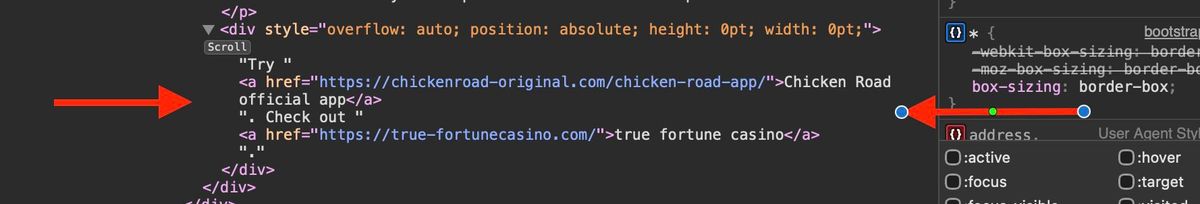
It's a block of links pointing off to sites that have nothing to do with the business. Spam, basically. Someone has got into the site and is using it to boost their own rankings, borrowing whatever trust and search history the site has built up over the years.
The clever (or annoying) bit is the inline style wrapped round it. That's there to keep the rogue content off the visible page. So you load the homepage in your browser, everything looks normal, and you carry on with your day.
Why nobody spots it
This kind of hack is designed to be quiet. The people who did it don't want your site to fall over or show a big skull and crossbones. They want it to keep running for as long as possible, because a working, trusted site is what's useful to them.
So the content is hidden from people but left in the HTML, where search engines and bots will still read it. You won't see it. Your editors won't see it. Google will.
That has knock-on effects you might not link back to the cause:
- Your search rankings drop for no obvious reason
- Google flags the site, or shows odd results under your domain
- Your domain gets associated with whatever dodgy sites are being linked to
- Whoever got in may still have access, and spam links might be the least of it
That last one is the real worry. If someone can put content on your homepage, it's fair to ask what else they've had access to.
How it gets there
When a Drupal version is supported, the Drupal security team finds and fixes vulnerabilities and puts out security releases. Apply those and you're covered for the known stuff.
Once a version goes end-of-life, that stops. Problems are still found in the code those versions share with newer releases and in the contrib modules they use, but nobody is patching the old versions anymore.
The fixes for newer versions are public, which makes things worse. Anyone wanting to break into older sites can see what was fixed and go looking for sites that never got the fix. That's automated, so it's not about whether your site is interesting enough to target. Bots scan everything.
In short, an EOL site isn't a question of if, it's a question of when.
A few quick checks you can do
You don't need to be a developer to get a feel for whether this applies to you.
- Find out your Drupal version. Log in as an admin and look at Reports > Status report. If it says 7, 8 or 9, you're on an unsupported version.
- View the source of your homepage. Right-click, View Page Source, and have a scroll. Look for links to sites you don't recognise, especially inside anything with display:none or text positioned way off screen.
- Search Google for your own site. Try site:yourdomain.co.uk and see if anything odd turns up, like pages or titles in other languages or about products you don't sell.
- Check Google Search Console if you have it set up. Security issues and manual actions show up there.
If any of that throws up something strange, don't just delete the snippet and move on. It'll probably come back, because the hole it came through is still open.
So what should you do?
If you're running a site on an EOL version of Drupal, please be aware that it is at real risk. Not theoretical risk, real risk, as this example shows.
The proper fix is to get onto a supported version and keep it updated. If the site has already been compromised, that also means a clean-up: finding and removing the injected content, working out how they got in, and closing the door behind them so it doesn't happen again.
Upgrades from older versions can sound daunting, Drupal 7 especially, but they're very doable and we've done a lot of them.
As always, if I've just described your site, we are happy to help :)
FAQs
Frequently asked questions
Drupal 7 reached end of life in January 2025, so the Drupal security team no longer fixes its security holes. It may still work, but any new problem found in core or its modules stays open on your site. The longer you wait, the bigger the risk and the bigger the upgrade.
As AI coding tools advance more and more security flaws are being exposed, Drupal 7 will not receive any official fixes for these.
Yes and No. Drupal 8 and 9 are both End of Life, and neither are receiving security updates. The good news tho is that Drupal 8 and later share the same foundations, so getting to the latest version is an upgrade, not a rebuild. We update your code and modules one major version at a time, and your content stays where it is.
Drupal 7 is different: it has to be migrated into a new site.
It depends mostly on how many contributed modules and how much custom code your site has. Try the upgrade calculator on this page for a rough figure. We'll give you a fixed scope and price after the audit, before any work starts.
We go through every module, theme and piece of custom code on your site. For each one we tell you whether it has a modern equivalent, needs rewriting, or can go. You get a written plan with costs, so you can decide before committing to the upgrade.
No. We migrate your content, files, users and URLs. If a URL has to change, we add a redirect so links and search rankings carry over. We run test migrations before launch so you can check everything is there.
Yes. We build the new site alongside the live one and keep content in sync. We then run a final migration just before launch, so editors only need a short content freeze, if any.
You can, and it's often a good moment to do it, especially coming from Drupal 7 when the theme has to be rebuilt anyway. We'll show you what an upgrade alone costs and what the extra work adds, so you can choose.
Typically we can include a light redesign or refresh for no extra cost.
For complex sites with lots of content types, permissions or integrations, Drupal is usually still the right choice. If your site is mostly marketing pages and articles, a headless CMS such as Sanity or Payload with a fast front end may be simpler and cheaper to run. We'll give you an honest recommendation as part of the upgrade audit.
